Addovation DocAgent - White Paper
Last Updated: 2026-10-06
Introduction
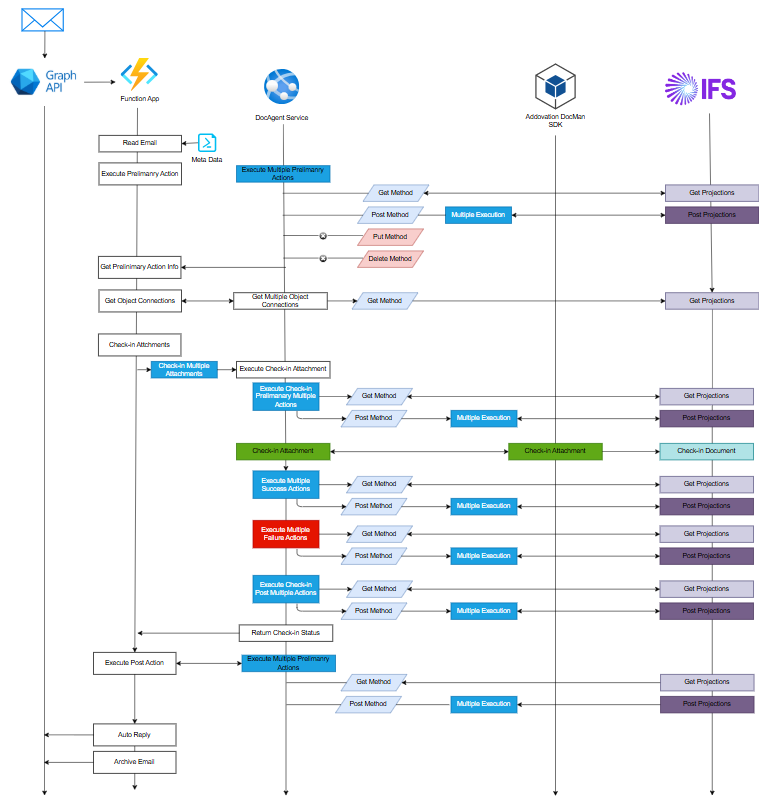
DocAgent is a schedule-based automation platform that monitors a customer's specified email account, reads incoming e-mails, and checks in any attached documents to IFS. Each e-mail is handled according to rules and business logic that the customer defines through the Addovation Cloud Portal. These rules can be applied before an attachment is checked in, to prepare it, or after check-in, for example to automatically release the document once it has been checked in to IFS.
Each e-mail account operates under a channel, and a channel holds all of the customer's configurations, including business logic, encrypted IFS access details, email account settings, auto-reply configurations, error handling policies, and GDPR compliance policies. Each channel is configured and operated independently, serving its own specific purpose.
Access to e-mail accounts is secured with Multi-Factor Authentication, and DocAgent uses the Microsoft Graph API to read e-mails securely and flag each message as read once it has been processed. Every e-mail that has been processed, whether successfully or not, is moved out of the inbox into its own designated folder, so no e-mail is ever lost during processing.
DocAgent also allows customers to block specific e-mail addresses from being processed, and to allow or skip specific attachment file types from being checked in, based on their own requirements.
All processing activity is logged to Azure Application Insights, allowing any suspicious activity or the cause of a failure to be traced back. All backend processing is accessed exclusively through secured Azure API Management (APIM) endpoints, and only authorized channels are permitted to access the APIM, which increases security and allows rate limits to be configured to guard against cyber-attacks.
Architecture
Addovation DocAgent System Architecture
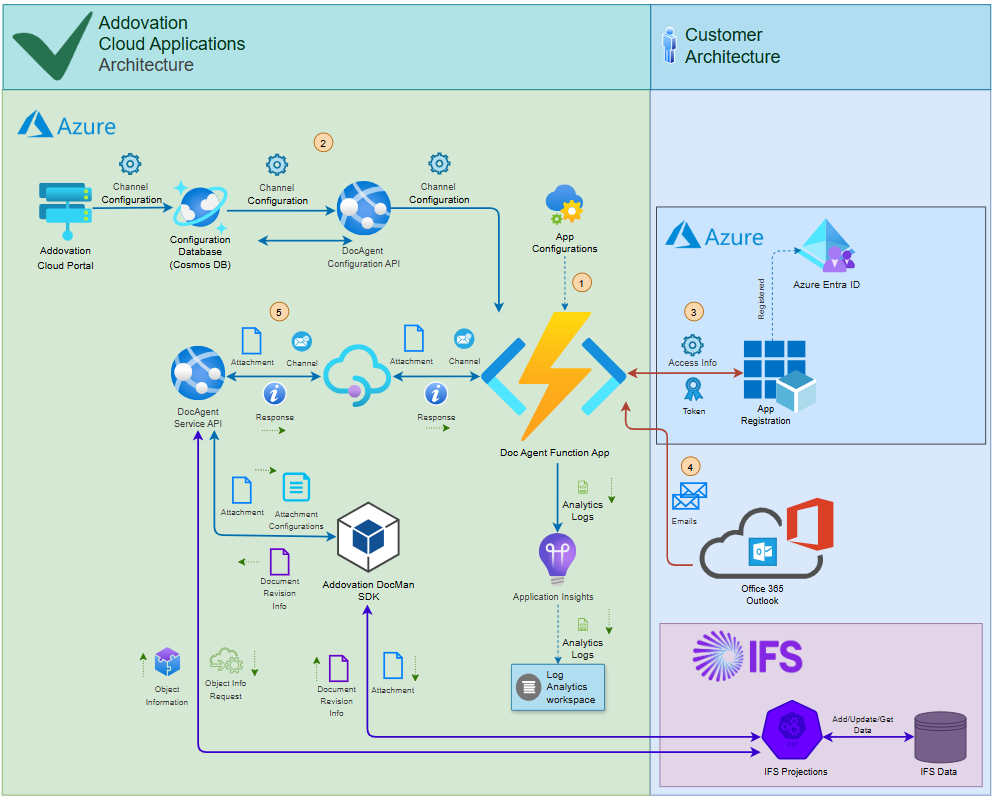
- Essential configurations required for the Function App are stored in its environment variables.
- Environment-related details are retrieved from subscription configurations.
- An access token is requested via Azure App Registration.
- The access token is used to fetch all emails from the inbox.
- Each email is processed to either create a new case or update an existing one.
- Message files and attachments (if configured) are checked-in into the corresponding object.
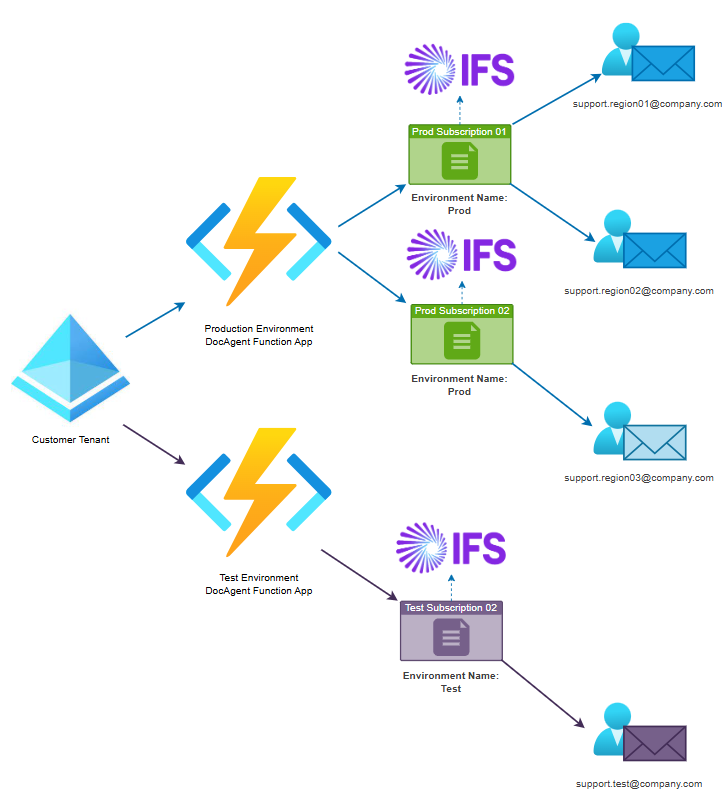
Addovation DocAgent - Multi Environment Support
Addovation DocAgent - Functional Flow
Addovation DocAgent - E-Mail Authentication
Addovation DocAgent supports Multi-Factor Authentication (MFA) through certificate-based authentication.
Multifactor Authentication Support (MFA)
Addovation DocAgent supports Multifactor Authentication (MFA) through certificate-based authentication, allowing the customer's email account to stay fully MFA protected while DocAgent still reads and processes emails securely end-to-end, with no username or password ever required.
MFA Authentication Architecture
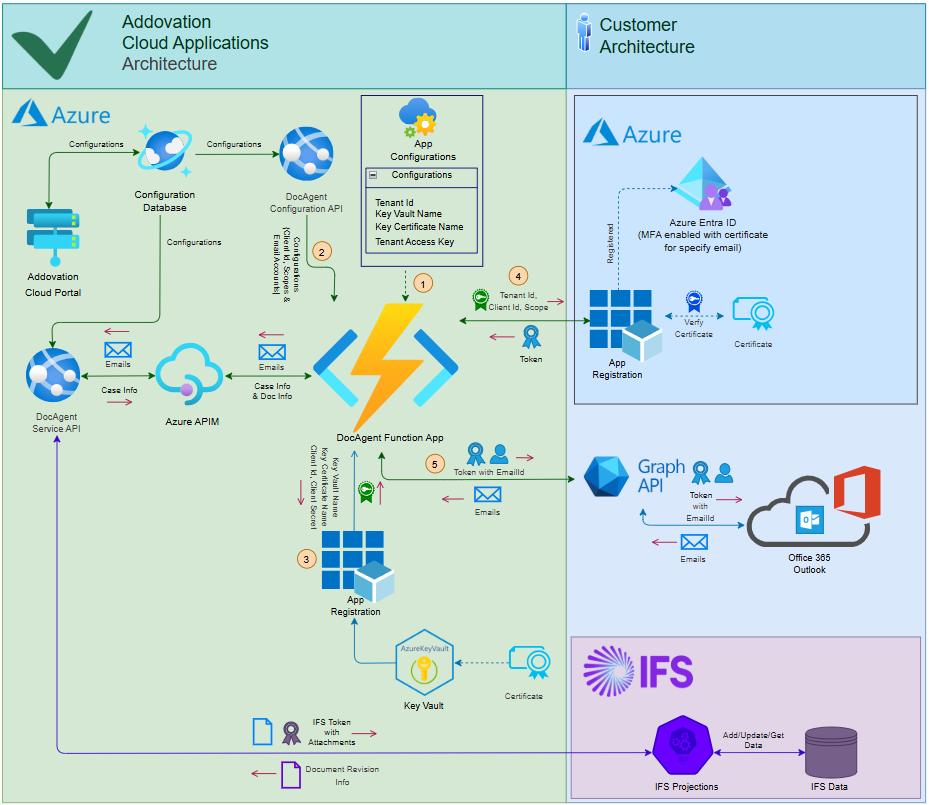
- The
Tenant ID,Key Vault Name,Certificate Name,Tenant Access Keyare stored in the Function App configurations. - The
Client ID,Scopes, andEmail IDare stored in the subscription configuration. - Using the
Key Vault NameandCertificate Name, the Function App retrieves anX509Certificate2certificate. - The retrieved certificate, along with the
Tenant ID,Client ID, andScope, is sent as request parameters to obtain an access token from the Azure App Registration. - The access token is then used to read and send emails using the specified
Email AccountusingMicrosoft Graph API
Security, Monitoring and Access Control
Addovation DocAgent is built so that every backend request, every processed e-mail, and every configuration change can be traced, controlled, and protected.
API Access Control
All backend processing is accessed exclusively through secured Azure API Management (APIM) endpoints. Only authorized, subscribed channels are permitted to call these endpoints, and configurable rate limits can be applied per channel to protect the service against abuse or cyber-attacks.
Activity Monitoring
All processing activity, successes, errors, and warnings, is logged to Azure Application Insights. This gives customers the ability to query log history and back-track any suspicious activity or the root cause of a failed case, in line with the GDPR compliance policy described below.
Technologies supported
The following technologies are supported or used by Addovation DocAgent.
E-Mail Access Methods
- Microsoft GraphAPI
Microsoft Azure technologies used
Host by Addovation
- Azure Function App
- Azure App Services
- Azure API Management
- Azure Cosmos DB (Core SQL)
- Azure Entra ID - App Registration
- Azure Key Vault
Host by Customer
- Azure Entra ID - App Registration
Requirements
Access Requirement
- A valid
subscription keyis required to provide authorized access to Addovation DocAgent Service API and Document Management API
E-Mail Account Requirement
- A
valid E-mail accountis required to process Addovation DocAgent functions.
Multifactor Authentication Requirements
- A
Azure Key VaulttoCertificateand be accessible forFunction App. Azure Entra App registrationcertificate-basedaccess levelApp permissionshould be provided to read and send emails for specific users
Channel Requirements
- Mandatory configurations are required to run a channel in an active state
- A
tenant Idrequired to configure in order restrict channel for customer tenant - A unique
Environment Namerequired per tenant to support multiple Function Applications - A
unique Channel nameis required per each tenant Id - At least one
unique e-mail accountis required per channel
IFS Information Requirements
- The service requires
IFS server extension - IFS projections should be published, and endpoint must be presented along with required fields to configurations.
Object keyvalues required to configure in Map Fields.IFS default valuesrequired to configure in Map Fields.- Any required fields required properly configure in Map Fields.
IFS Access Requirements
- A service user in IFS with required permissions
- IAM client account with connected to specified service user
Document Management Service Requirements
Document classrequired, if document check-in is enabled.Document formatis option but requires if customer wish to check-in documents for a certain document format.Document Typeshould be available in EDM basic data for MSG or EML formats, depends on Mail Format configuration.Document Typeshould be available in EDM basic data for any document type customer wish to check-in as attachments.Logical Unit Name (LuName)andKeyRefrequired properly configure to check-in documents.
Networking Requirements
By default, the service supports the following networking options:
- Azure Virtual Network and
- Azure site-to-site VPN
This is required for communication between your IFS instance and the Addovation Cloud.
Other networking technologies can used. Contact us for more information.
Azure Configuration Requirements
If customer wish to publish DocAgent on their premise, an azure portal is required with a subscription and subscription pricing plan which allow will to create and maintain following resources
- App Registration
- Resource Groups
- Azure Function
- Azure Storage
- Azure App Service
- Key Vault
- Azure Insights
- Log Analytics Workspace
Windows Operating system should support in azure portal alone with
.Net 8 or higher for app services and Azure Functions
IFS Applications Requirements
We currently support the following ERP systems:
- IFS Cloud™ 21R1, and later
Data CRUD operations are performed using IFS projections, therefore Addovation DocAgent service endpoint must be whitelisted in IFS environment.
GDPR Compliance
Addovation DocAgent is built with GDPR regulations in mind and keeps a minimum of information by default.
The following is logged in the customer's Azure Application Insight logs:
- Tenant Id
- Tenant Name
- E-Mail Id (email address of the configured channel)
- E-Mail Message Id (unique id)
- E-Mail Subject
Addovation DocAgent requires the information listed above to monitor and resolve problems (information, errors and warnings) such as when an e-mail fails to process, the IFS server does not respond, e-mail account authorization fails, or other problems processing incoming e-mails.
In addition to the information above DocAgent can be configured to log additional information when a customer or the situation requires it and these values are optional. The following fields may be logged:
- Sent From (e-mail address)
- Display Name (sender's name)
- Description (message body)
- Mail Direction (In/out)
- Sent To (email addresses)
- Sent To CC (email addresses)
- Message Date
- Customer Name (customer in IFS which is connected to the contact/sender)
Limitations
- Addovation DocAgent supports Microsoft 365 (Exchange Online).
- The service checks e-mail at a rate limited by the customer's e-mail system
- The service is based on having a single e-mail account (address) as both Sender and Channel, which means that a shared e-mail Group account cannot be used
- The maximum attachment size supported is
150 MB. - Addovation DocAgent has the same restrictions and validation requirements as the customer's IFS application.
- IFS must be configured (Basic Data) in order for the Addovation DocAgent to store information in the customer's Logical Units (for example DocMan and CallCenter).
- An e-mail account cannot be used in multiple channels under any circumstances.
- Invalid or incomplete configurations might not provide the expected result in IFS.